By the Greymatter.io Technology, Innovation, and Outreach Team
In a prior blog, we explained how Greymatter supports the security analytics and intelligence layer of Gartner’s Cybersecurity Mesh Architecture (CSMA)1. Here, we’re going to focus on our support of the identity fabric layer, arguably the most important layer of CSMA because it is the backbone. It provides a unified, integrated approach to identity and access management (IAM).
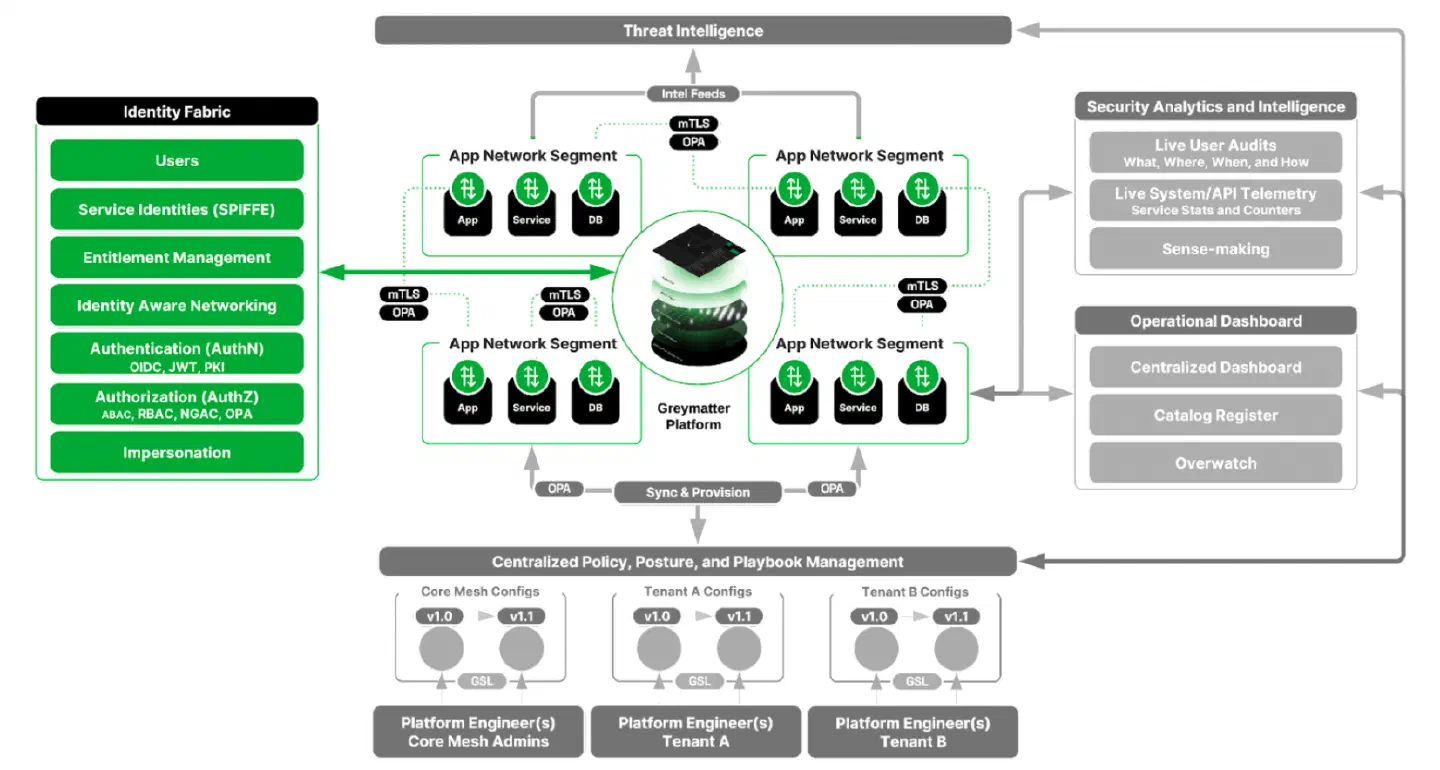
Figure 1: CSMA and Greymatter
Why now
Managing user and system identities and access in today’s hybrid, multi-cloud environments is incredibly complex. Organizations often have IAM solutions from multiple, external identity providers to manage different types of identities, applications, and access requirements. This results in siloed and fragmented identity management environments, which can lead to inefficiencies, security risks, and compliance issues.
Furthermore, applications often use different authentication and authorization mechanisms, leading to gaps in identity awareness. Auditing varies by code or app, making it hard to track user identity across the network. Although OIDC is common, token exchange is limited. Organizations must pass large user claims to all assets, even when unnecessary. This broad identity propagation reveals access levels and creates new attack vectors for threat actors.
The CSMA identity fabric layer tackles growing complexity and breaks down silos. It promotes centralized identity and access management. At the same time, it allows identity segmentation by location, application, service, or network asset.
Why Greymatter.io
Greymatter unifies the identity fabric layer. It provides a consistent view of identities, access controls, and policies across the entire environment. Clients can improve security, simplify compliance, and simplify IAM operations. Here are a few top use cases.
Secure service-to-service communication
Organizations struggle to secure their microservices-based architecture and make sure that only authorized services are communicating to each other. Implementing and managing service-to-service communications for every transaction, in compliance with their security policies and industry regulations, is incredibly complex and time-consuming. And the challenge mounts as new services and capabilities are introduced. Greymatter removes complexity and improves security. It provides service-to-service identity attestation, certificate rotation, and policy enforcement out of the box to help prevent unauthorized access to sensitive data and transactions.
Identity management across hybrid and multicloud environments
Today, 87% of organizations have a multi-cloud strategy2, and each cloud environment has its own IAM solution. What’s more, many organizations continue to operate on-premises infrastructure. IAM solutions differ, and that creates a management challenge. Teams move between IAM solutions that each show identities, access controls, and policies in a different way. Greymatter supports OIDC compliant interfaces, so you do not need to manage separate IAM solutions. You get one view of identities and access controls across multiple clouds and hybrid environments.
Identity and claims segmentation
Highly regulated industries such as healthcare and financial services must balance employee access with regulations such as HIPAA, GDPR, and PCI. This balance can be difficult. Greymatter identity and claims segmentation helps institutions strike that balance. Each application and service gets only the identity attributes and access controls it needs. Access depends on employee role and location, which reduces the risk of exposure. Also, all interactions are logged and stored providing transparency and auditing capabilities.
Role-based and fine-grained access control
The move to a Zero Trust framework often entails looking into adopting a role-based access control (RBAC) and attribute-based access control (ABAC) model. Adding yet another layer of tools to their tech stack to manage isn’t something most teams are eager to do. To make RBAC and ABAC simpler to adopt, clients can use Greymatter support for Open Policy Agent (OPA). They define RBAC and ABAC policies for fine-grained access control that fits their requirements.
Centralized identity infrastructure
In an effort to unify their IAM environment, organizations increasingly choose an IAM product that supports OIDC integration. However, they soon discover that most of their applications need to be updated to support the OIDC specification, which requires significant coding and developer time. This unplanned expense slows widespread adoption throughout the enterprise and pulls developers away from more strategic initiatives. Greymatter simplifies the process with built-in support for OIDC authentication and authorization capabilities, so integration is fast and simple.
How Greymatter does it
As an application networking platform, Greymatter supports the CSMA identity fabric layer. Organizations manage identities and access controls centrally across hybrid and multi-cloud environments, while enforcement stays decentralized and simple. Specifically:
User Identity
- To validate user identity, organizations use various authentication mechanisms, whether PKI, MFA, OIDC, JWT tokens, or something else. Greymatter has built-in support for OIDC. It brings different authentication methods and tools together. Authentication then flows through the network based on the user and the service, application, or data they need.
Service Identities
- Within Greymatter, each service also receives its own identity. Greymatter’s SPIFFE/SPIRE integration enables automated and secure issuance and revocation of identity certificates for services. Control over service identities helps to prevent unauthorized access to sensitive data and transactions within the microservices environment.
Least-Privileged Access
- Using an organization’s need to provide least-privilege access policy models, policy layer, Greymatter uses the access control approaches that security teams write in Open Policy Agent (OPA) Rego. These include role-based (RBAC), attribute-based (ABAC), and next-generation (NGAC) access control. This helps offload the work for development teams. Every service that is tied into the Greymatter application networking platform can benefit from the organization’s centralized policy engine and fine-grained access controls.
Entitlement Management
- We further strengthen security by rotating service identities on an hourly or configurable basis. In the event of a service compromise, entitlement management reduces the blast radius and lowers risk. Threat actors must regain access to the service, and organizations get a better chance to detect a compromise.
Authorization
- Greymatter enables identity-aware networking by understanding and propagating user and system identities across hybrid and multi-cloud environments. It unifies identities from providers like Keycloak, Okta, Google, and Microsoft, granting access based on role and location.
- We make it simple for organizations to use Open Policy Agent (OPA) to write and configure RBAC and ABAC authorization policies for each service at a granular level through a centralized, repeatable process. Integration with Greymatter makes sure that only authorized users have access to specific resources, for example applications, APIs, and sensitive data. Access can be automatically blocked based on contextual data such as request payloads, device posture, location, and more.
Impersonation
- Greymatter supports impersonation for additional security, whereby authorization to access a service is dependent on their having already accessed another service. Access controls are defined so that if a user tries to access that service directly then access is denied. Linking the user and service together provides additional fine-grained controls and is simple to configure as part of Greymatter’s role-based access control configurations.
Additional capabilities include scalability, high availability, logging of authentication activity, complete auditing, and integration with security tools. Greymatter provides a battle-tested identity fabric suite, supporting organizations today and as their IT environments grow.
What’s in it for our clients
Our clients gain meaningful value from our early support for CSMA’s identity fabric layer, including:
- Improve threat detection and response by removing silos. Gain real-time visibility into who’s doing what, where, when, and how for faster action.
- Resolve incidents faster with detailed logs. Track interactions between users, services, and data, and export logs to security tools for analysis.
- Maintain compliance with fine-grained controls. Support standards like NIST 800-207/207A, GDPR, HIPAA, and PCI with transparent, auditable capabilities.
- Save costs by simplifying operations. Reduce IAM tools, development time, and breach-related expenses.
We’re expanding our federated identity, fine-grained access control, and identity-aware networking capabilities. Organizations will gain broader visibility into their identity landscape. This will simplify managing user and service identities, access policies, and network security. It also improves identity management efficiency, giving infrastructure teams a smooth experience. As a result, teams can focus more on critical tasks.
In our next blog, we’ll specifically address how Greymatter connects and contributes to CSMA’s centralized policy, posture, and playbook management layer.
Contact us today to schedule your free consultation, determine your microservices maturity level, and build a reference implementation architecture. This moves your organization up the microservices maturity model, so you deliver software faster and reach market sooner, with security built in.