Greymatter.ioGreymatter.io
Start for Free
Greymatter.ioGreymatter.io Why Greymatter.io?
Pricing Start for Free
Platform • Mesh

Lower cost. Lower risk. Fewer gaps.

Run your whole mesh from one policy, not a stack of tools and the scripts that join them. Greymatter encrypts and covers every app, including the ones nobody remembered.

Production Platform 88 svc · 12 ns Search 758 objects across 8 types ▲ 6 degraded● 747 healthy
The Grid › spire-opencostPod cardsNetwork graphread 2:05:37 PM EDT · every 15s
Port All ports ⌄flow-ledger · 6 raw rows · 5 shown · updated a few seconds ago
Tier 0 · 2 Tier 1 · 2 Tier 2 · 2
ext:envoy-gateway-●●●●not managed by Greymatter
spire-grafana-prometheus-serverin the mesh
TLS · to :10908 mTLS · TLS 1.3 · PQ · to :9003
Spire Opencost EdgeDEPLOYMENT
Running1 pod · 1/1 ready
2 services2 direct · 0 wider
Human CuratedGSL
opencostDEPLOYMENT
Running1 pod · 3/3 ready
3 services1 direct · 2 wider
Strict MeshAutoCalls 3 workloads
mTLS · PQ · :9090 TLS · to :443
athena.us-west-1.amazonaws.com
pricing.us-east-1.amazonaws.com
Workloads 6mTLS 50%Observed now 0.12 calls/s
Console view · sample data. We masked names and identifiers.
The DIY disappointment

A do-it-yourself service mesh leaves gaps.

Close the gaps a hand-built mesh leaves open.

Tap a card to see how Greymatter fixes it.
Every seam is a way in

Separate gateway, mesh, and security tools, stitched across clouds. Each hop between them is a seam no single tool protects or monitors.

Tap to reveal →
Solved. One platform, no seams.

Run the gateway, mesh, and security together in every cloud. Greymatter encrypts and records every hop.

Greymatter solves it
Upkeep eats the budget

Clouds, clusters, and add-on tools all need their own upgrades, patches, and rules. Teams spend more time keeping the network running than building on it.

Tap to reveal →
Solved. One flat cost.

Every capability and full support, including security patches, for one price. No plugins. No add-ons.

Greymatter solves it
One person holds it together

One engineer wrote the scripts. Only that person understands them.

Tap to reveal →
Solved. It runs itself.

Services are set up and maintained for you. No scripts to write. No single engineer to depend on.

Greymatter solves it
While you were reading this

A system went down. A certificate rotated. You handled neither.

An autonomous mesh keeps your apps running, encrypted, and accounted for, with far less for anyone on call to do.
Full coverage, zero setup +

Label a project once, and its apps join automatically. The app an attacker would find first is already protected.

Try a new version on a small share of traffic first. If something looks wrong, switch everyone back with one change. A bad release reaches a few requests, not your whole user base.

Every service shows its blast radius: the apps, APIs, AI agents, platform services, and infrastructure that depend on it. Before a change, you know what it could touch. When something fails, you know what is affecting your customers.

Traffic between your apps gets post-quantum protection from the start. Certificates renew on their own, so nothing lapses. This protection is FIPS 140-3 validated (CMVP #5191), and no setting turns it off.

When a service fails, traffic shifts to the backup you chose. Failed requests retry on their own. No manual rerouting, no 2 a.m. scramble.

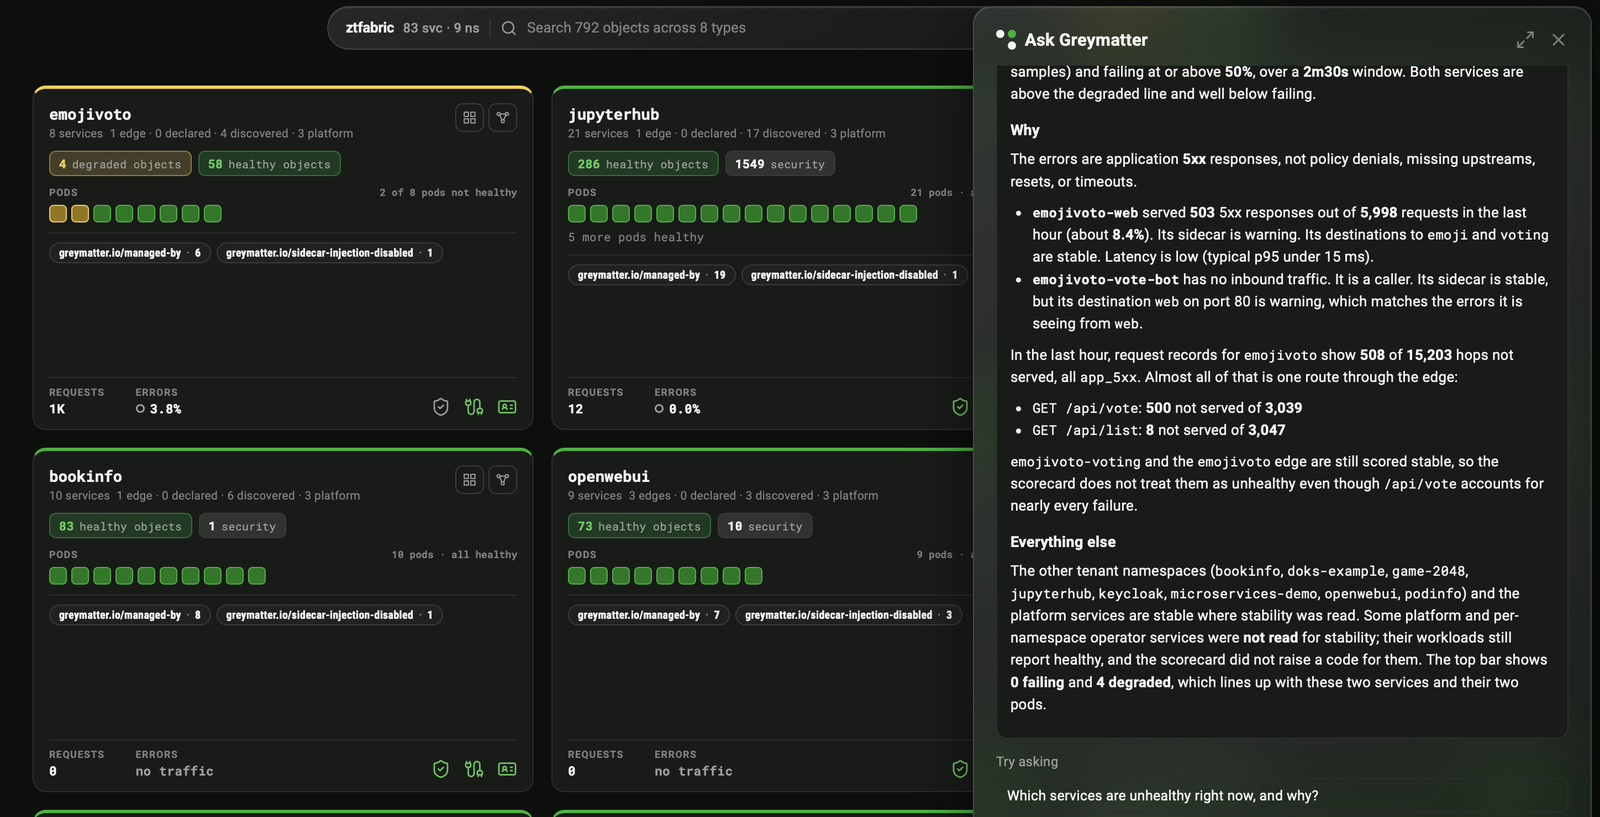
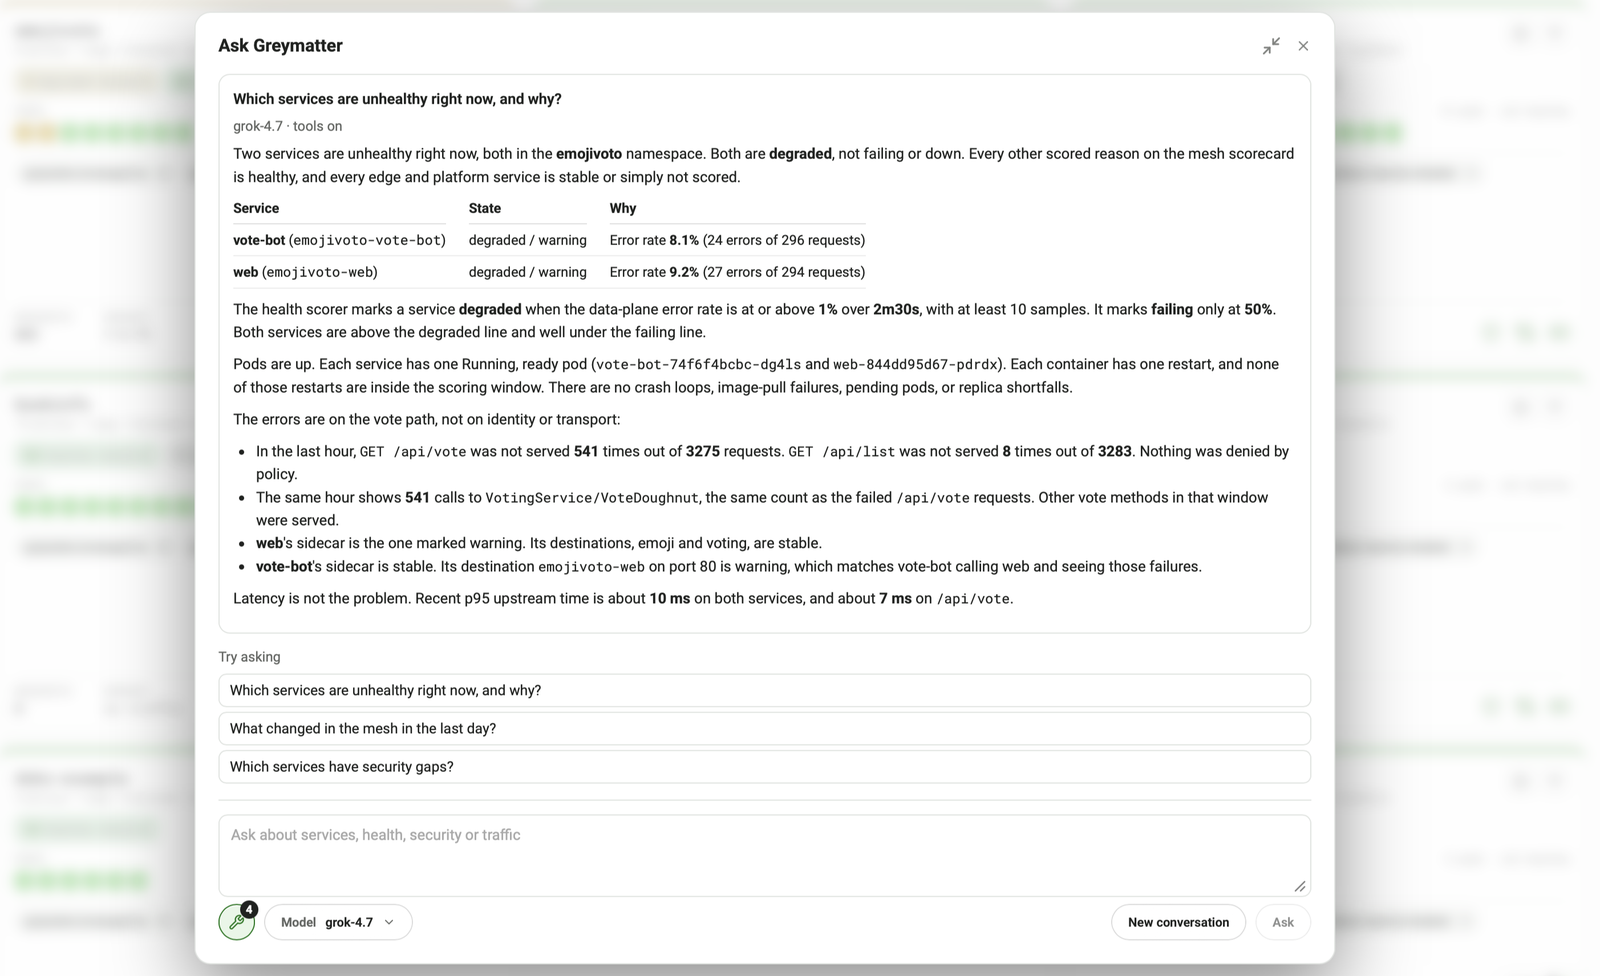
Ask Greymatter answers questions about your mesh in plain language, from the platform’s own data. Ask what is failing, what changed, or what breaks if a service goes down. Your team finds the cause sooner and recovers faster.

Production Platform 88 svc · 12 ns Search 758 objects across 8 types ▲ 6 degraded● 747 healthy
The Grid › spire-opencostread 02:57:52 PM EDT · every 3s● 5
spire-opencost5 services · 1 edge · 0 declared · 1 discovered · 3 platform
39 healthy objects
PODS5 pods · all healthy
greymatter.io/managed-by · 3greymatter.io/sidecar-injection-disabled · 1
REQUESTS
2
ERRORS
○ 0.0%
greymatter.io/managed-by carried by 3 workloads
Click to pin, then select or copy
opencostns: spire-opencost
DEPLOYMENT
Running1 pod · 3/3 ready
PODCONTAINERS
opencost-78677c8fb6-●●●●
BLAST RADIUS3 services1 direct · 2 wider
1 podStrict MeshAuto
Configured by the platform’s defaults from the onboarding policy.
Click to pin, then select or copy
Learn. Preview. Seal.

The safe road to Zero Trust.

Switching apps to secure-only connections is where most teams stall. No one knows which services will suddenly stop working. Greymatter learns your live traffic and lists the links that would be refused, before anything changes.

Full lockdown becomes a planned event, not an outage risk.
01 · LearnStrict Mesh
0.0.0.0:10908TLSmTLSSPIRE
ALLOWLIST
any valid mesh identity · 4 learned
jupyterhub-hub (self)
jupyterhub-jupyter-admin
jupyterhub-jupyter-q-example-com---bda6a6b7
jupyterhub-proxy

Every app, mapped

  • No app left out · late additions get the same protection as the rest
  • No waiting on busy teams · coverage does not depend on who has time to opt in
  • Protected at launch · new apps never run unprotected while a ticket waits
  • Traffic learned, not guessed · see who talks to your apps, from real requests
02 · PreviewAllowlist
0.0.0.0:10908TLSmTLSSPIRE
If enforceIdentity is enabled, the learned identities become the allowlist.
PER-PORT ALLOWLIST
:8081
jupyterhub-hub
jupyterhub-jupyter-admin
jupyterhub-jupyter-q-example-com---bda6a6b7
jupyterhub-proxy

No surprise outages

  • Know before you lock down · see which connections strict mode will refuse, before it does
  • Approve the stragglers · grant access in advance, so nothing breaks on the day
  • Lockdown on your date · you pick the day strict mode turns on
  • Exceptions in the open · any app that skips protection is a line someone approved
03 · SealEnforced
hub
ns: jupyterhub
DEPLOYMENT
Running1 pod · 2/2 ready
PODCONTAINERS
hub-5856c59646-fs7vt
1 podStrict IdentityAuto

Locked in, with proof

  • No backsliding · a restart never loosens the protection you reached
  • One rulebook · your platform team sets the minimum once, and no team can set a lower level
  • History nobody rewrites · only the platform writes the record, so no one edits it quietly
  • Ready for the next site · what the mesh learned becomes a file your team owns. New clusters start protected from their first app.
Fits what you run

Runs on the Kubernetes you already have.

In the cloud, on premises, or offline. Red Hat OpenShift too.

Install it from the OpenShift console your team knows.

Runs on
OpenShift
Kubernetes
RKE2
AWS
Installs with
Helm
Argo CD
Flux
Git
Works with
SPIFFE/SPIRE
Kafka
Prometheus
Grafana
OpenTelemetry
Ready when you are

Stop assembling and maintaining a mesh. Start operating one.

Backup routes set once, with no scripts to maintain. Try it free on your own systems.

Start for Free Meet Our Security Experts Browse How to Buy →
Download the Mesh white paper
Go deeper

Additional resources

Use case Zero Trust Networking Learn More → Blog Greymatter.io versus Istio: What is the difference? Read the Blog → Video Inside the Service Mesh Market: A Conversation with GigaOm Watch the Video →
Swipe for more
Straight answers

Frequently asked questions

Yes. Greymatter runs on disconnected and air-gapped networks. It pulls images from a private registry you control.

Greymatter adds apps from one label on a project. The platform attaches to new and running apps, learns their traffic and encrypts their connections by default. Platform teams write the policy once, and app teams refine it within set limits.

Yes. Greymatter protects Kafka and other non-web traffic too. Your data streams get the same protection as your web apps.

Yes. Greymatter reads your mesh rules from Git. A teammate reviews changes, then Greymatter applies them to your cluster. To undo a change, restore the last good version in Git.

No. Greymatter installs with Helm and fits Argo CD and Flux workflows. Argo CD and Flux keep deploying your applications. Your mesh rules update alongside your apps.