How organizations build, deploy, and monitor applications has changed dramatically over the past several years. To speed up delivery, we moved from a monolithic architecture to a cloud-native approach. Our apps now run beyond on-prem data centers.
Piloting cloud-native
Teams began piloting microservices, containers, APIs, and agile development. The improvements in application delivery speed proved undeniable. But they soon hit road blocks. Separate programming language tools, development frameworks, and logging tools introduced complexity. Each microservice in a cloud-native environment is a separate application unto itself with limited control, security, and insight. As services moved into deployment, IT teams grew upset. They lacked control and visibility across hybrid and multicloud applications.
53% say complex implementations for multicloud and hybrid are a significant challenge.1
Kickstarting the path to distributed applications at scale
Service meshes are intended to address these challenges. And they have, to a degree. For static, small, Kubernetes environments, service meshes provide a de-coupled layer away from the application code. Service meshes aim to solve these challenges, and to some extent, they do. In small, static Kubernetes setups, they offer a de-coupled layer from app code. They manage configuration, route east west traffic, and enforce security across microservices, APIs, and data sources. However, as service volumes grow, distributed apps increasingly fail architectural reviews. This is often due to configuration errors, security flaws, and limited multicloud support.
More than half of security, DevOps, & dev professionals cite API security concerns for delayed rollout of a new service or app. 2
Service mesh is a starting point. However, it has been over hyped. On its own, it cannot address the complex software development, delivery, and oversight requirements that enterprise architectures demand. This is especially true across on-prem, container, hybrid, and multicloud environments, where providing zero trust application security remains critical.
99% of cloud-native environments have over privileged IDs.3
Organizations continuing their path to speed up software delivery, while providing security need more.
Enabling the hyper-dynamic enterprise
Today, multicloud is mainstream, and organizations in highly regulated industries still keep critical assets and data on premises. Teams in this complex era need an alternative to fragmented tools and open source solutions.
This is where an end-to-end, enterprise-grade application networking platform like Greymatter comes in. It’s completely platform-agnostic and container-agnostic to meet you where you are and serve as a bridge to the future.
As the number of APIs, apps, and microservices increase, and your control, security, and visibility decrease, it tackles software delivery complexity and risk. It succeeds where cloud provider-specific solutions cannot, across multi-cloud and hybrid environments. And although it builds on a service mesh as do first-generation platforms, it goes well beyond with less complexity. The platform delivers critical service connectivity layer (SCL) functions. Developers can focus on building great software without touching network plumbing or security controls, in line with the tenets of platform engineering.
With a head start working with the largest defense and intelligence agencies, Greymatter has built the most proven and complete, modern application networking platform.
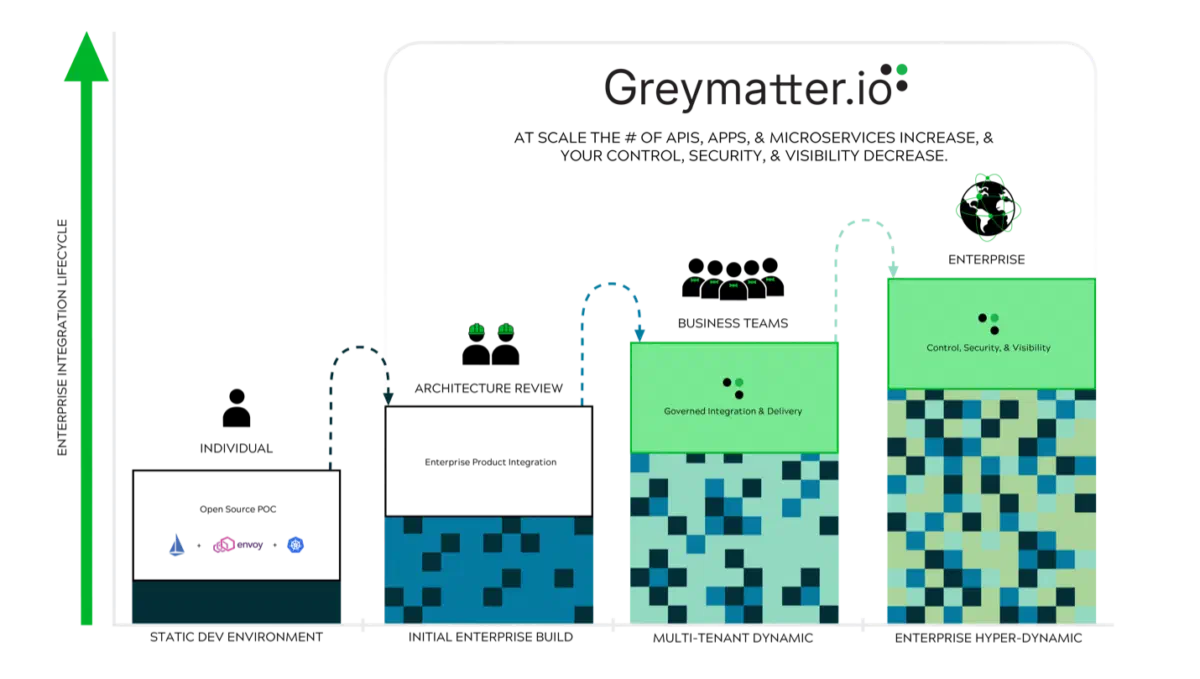
Fig 1. The Enterprise Integration Lifecycle
Greymatter’s Impact
It simplifies control, security, and visibility across multi-tenant and hyper-dynamic environments. It centralizes configuration management, provides identity-aware networking and complete audits with threat intelligence integration, and offers one dashboard for all operations. The result? It delivers on the promise of microservices architectures for greater application agility, flexibility, and scalability, by:
- Enabling rapid, reliable, and repeatable delivery of new software,
- Delivering cybersecurity mesh architecture for zero-trust security,
- Integrating with existing IT investments, and
- Enabling smarter business decision-making across the enterprise.
Wherever you are on your path, contact us to schedule your free consultation. We’ll start by helping you determine your microservices maturity level. Next, we’ll build a reference implementation architecture. From there, you’ll begin advancing your path to accelerate software delivery and increase speed to market. At the same time, you’ll gain greater control, stronger security, and improved visibility, with minimal configuration or code required.
Sources
- 1 Software AG Survey, February and March 2022; 1,150 respondents to Survey
- 2 API Security: Latest Insights and Key Trends, Google Cloud 2022 Research Report
- 3 2022 IBM Security X-Force Cloud Threat Landscape Report